Lesson 5 of 14 · 40 min read
Permissions and safety: limiting what the agent can reach
Permission modes, the auto-mode classifier and its limits, deny and ask rules that keep .env out of reach, and the OS sandbox around shell commands.
Code: shop-workspace and the four repositories its setup.sh clones, from the tag lesson-05-start to lesson-05-end. To get the demo, see lesson 1.
This chapter starts at the tag lesson-05-start in all five repositories. Run ./checkout-lesson.sh 05 from shop-workspace to put every repository there. If your copy drifts, run ./checkout-lesson.sh 05 --end from the same directory to jump every repository to lesson-05-end, the state the chapter finishes in. You need uv, Git, and a Claude account with Claude Code. No step in the lesson 05 recording uses Kafka, Docker, or a GitHub copy of the repositories.
This chapter was recorded on Claude Code 2.1.295 in October 2026. Documented defaults, limits, and labels are as of that month and may have changed since. The lesson 05 recording used Opus 5.5 (claude-opus-5-5) at medium effort in auto mode.
1. Chapter frame: reduced reach, not a guarantee
What the chapter promises
The chapter is about limiting what the agent can reach. It does not promise that the agent will never read a secret or damage your data. The documentation and the recorded runs do not support a claim that strong, and no control in this chapter is a complete guarantee. Each control is described together with the cases it does not cover.
How claims are marked
Each claim says where it comes from: 'the documentation says' marks documented behavior, which I paraphrase and which can change between releases; 'in the recorded run' marks what happened in the lesson 05 recording; and 'in my view' marks my own inference or recommendation. Model output is not deterministic, so a recorded response is one run, not guaranteed output.
An example from this chapter: in my view, you should review a generated Alembic migration before you apply it. The chapter cites no documentation for migration review.
Instructions are not rules
The documentation says CLAUDE.md is delivered to Claude as context, with no guarantee of strict compliance. A line in CLAUDE.md that tells Claude to leave .env alone is therefore a request. The permission rules in the next sections are configured settings, which is a different kind of control.
The chapter covers three controls, in this order: permission rules (allow, ask, and deny), the auto-mode classifier, and the sandbox.
2. Permission modes: which one a session starts in
The documentation lists six permission modes: default (shown as Manual), acceptEdits, plan, auto, dontAsk, and bypassPermissions. You have already used plan. The documentation says two things about rules hold across the list: deny rules apply in every mode, including bypassPermissions, and allow rules have no effect in bypassPermissions. This paraphrases the permission-modes page. The mode table on that page describes what each mode does, and it is the place to check default, acceptEdits, dontAsk, and bypassPermissions.
The starting mode
A session starts in auto mode. The release notes (the changelog) give two entries for this:
- Version 2.1.283 made auto the starting mode for sessions that use third-party providers or have telemetry turned off.
- Version 2.1.284 made auto the starting mode on every plan and provider, in the terminal and in VS Code.
The permission-modes page gives a different version: it says 2.1.283 for all sessions. Both sources are first-party and the discrepancy is unresolved, so this chapter follows the changelog for version-specific claims and tells you where the page differs. The sources also give 2.1.285 for claude -p and SDK sessions that run without feature flags.
The recording was made on 2.1.295, which is later than every version the sources give, so a session on 2.1.295 meets the version condition in each of them. If you run an older version, compare it with the entries above instead of assuming a starting mode. In the recorded run, the lesson 05 session ran in auto mode. Activity 1 turns this section into a short note you can reuse.
3. Rules for keeping .env and secrets out of reach
Permission rules are settings in .claude/settings.json. There are three types: an allow rule names actions to permit, an ask rule names actions to confirm with you, and a deny rule names actions to refuse. An ask rule asks. It does not block.
The documentation points to permissions.deny for actions that must never run. In my view, use a deny rule for .env. If several rules of different types match one action, which one wins? This chapter claims no order. Check the permissions page of the official documentation before you depend on one.
The rules from the recording
In the recorded run, Claude wrote the settings file from this prompt:
Create .claude/settings.json: allow uv run pytest, ruff and mypy; ask before git push; deny reading .env and .env.* files. Add .env to .gitignore.The two rules from the recording that this chapter works with, listed by type:
deny  Read(./.env)
ask   Bash(git push:*)
These are the rule strings, not the file layout. Open the file Claude wrote and look for each string under its type. The prompt also asked for allow rules and for .env.* files, so the file may hold more than these two rules.
In my view, add a third rule that denies edits to the same file:
deny Edit(./.env)The recorded prompt asked only to deny reading .env and .env.* files, so the recording gives no Edit rule. The Edit rule is my addition. Treat it, and any further pattern, as an extension of your own: check its spelling against the permissions page and note the section heading you used.
In the recorded run, the ask rule was written as Bash(git push:*). The documentation describes :* as an equivalent trailing wildcard, so it reads like Bash(git push *).
Which directory a pattern anchors to
The documentation says a relative Read or Edit pattern such as ./.env anchors at the current directory, not at the repository root. A pattern with a single leading slash anchors at the settings source, not at the filesystem root. When you report what a rule covered, name the directory the session started in, because that decides which .env the pattern points at.
In the recorded run, Claude said the Read(./.env) rules cover only the repository root. That matches the documentation when the session starts at the repository root. The recorded session ran in orders-service, so there the repository root is the orders-service directory. If you scope a session to one service, as you did earlier, name that service's directory. Activity 2 asks you to write yours down.
Testing the rules
In the recorded run, cat, wc, and grep on .env were denied with the deny rules in place. The recorded prompt for the cat step was Try cat .env.. Model output is not deterministic, so compare your results with these and report them as your run.
Use a .env that holds placeholder values only. In the recorded run, the .env held a random throwaway value that was never printed. Do not put a real secret into the demo.
What these rules do not cover
A rule is one control for a named set of tools, not proof that a file is unreachable. The next section lists the cases that stay open, including two spellings of git push that a Bash rule for git push does not match.
4. What deny rules and Bash rules do not cover
The documentation says that Read and Edit deny rules cover three things:
- Claude's built-in file tools.
- Recognized Bash file commands:
cat,head,tail,sed, andtee. - Redirection targets.
It also says they do not cover two things:
- Commands that read files without naming them, such as
grep -r. - Scripts that open files themselves.
In the recorded run, cat, wc, and grep on .env were denied. The documented list of recognized commands names cat, head, tail, sed, and tee, and it does not name wc. Both facts stand as written. This chapter does not explain why wc was denied, and it does not add commands to the documented list. A denial in one run is not a promise that the same command is always covered.
Bash rules match text
The documentation says a Bash deny or ask rule matches the command text Claude writes. It is not a security boundary around the program. The documentation's example is that Bash(git push *) does not stop git -C . push or git -c push.default=current push.
In my view, the ask rule from the recording, Bash(git push:*), has the same shape, so those two forms are not covered by it either. The documentation describes :* as an equivalent trailing wildcard. My conclusion about these two spellings applies that description; the documentation does not test it. Do not run a push to check it.
Content that skips the rules
In the recorded run's notes for lesson 05, content pasted into a prompt, or entered with the ! prompt, enters the conversation, and no deny rule protects it. The documented list above names the built-in file tools, recognized Bash file commands, and redirection targets, and it does not name pasted or ! content. The documentation says separately that a command typed at the ! prompt runs unsandboxed in most sessions.
In my view, do not paste secrets into a prompt, and do not run ! commands that print them.
The documentation names the sandbox as the OS-level enforcement. It has its own section after the classifier, together with its own gaps.
5. The auto-mode classifier: a second gate
Auto mode puts a second model between Claude and some actions. The documentation calls it the classifier. By default it is Claude Sonnet 5, and it is a separate model from the one your session runs on.
What it reviews
The documentation says:
- The classifier reviews actions after the rules and the read-only and in-directory checks.
- It sees your messages, the tool calls that are not read-only, and CLAUDE.md.
- It does not see tool results, which are stripped.
- Broad allow rules such as
Bash(*)andBash(python*)are dropped when you enter auto mode. - Three blocks in a row, or 20 in total, pause auto mode.
A second gate
The documentation calls auto mode a second gate. For actions that must never run, it points to permissions.deny, which is the deny rule type from the previous sections. In the documented decision order, the classifier reviews actions after the rules.
Anthropic's March 2026 post, published 2026-03-25, reported 0.4% false positives and 17% false negatives on real overeager actions for the pipeline current at that time. The figures are volatile: they describe that release and carry that date. This chapter does not present them as the current classifier's rates, and whether they still describe it is not established. The chapter paraphrases the figures; check the post before you quote them.
What the classifier does not cover
- It is not a guarantee. The published figures include misses.
- It does not see tool results.
- Repeated blocks pause it.
The figures carry their own date, 2026-03-25. Re-check the model, the dropped-rule behavior, the thresholds, and the figures when you rely on them. Activity 4 asks you to write the fact sheet.
6. The sandbox: an OS boundary around shell commands
The documentation says that the sandbox is an OS-enforced boundary around shell commands (Bash, PowerShell, and Monitor) and their processes only. File tools, MCP servers, command hooks, and plugin processes run outside it. A command typed at the ! prompt is a further case, described in the section on what deny rules and Bash rules do not cover.
The mechanism depends on the platform: macOS uses Seatbelt, Linux and WSL2 use bubblewrap, and native Windows runs unsandboxed.
Two scopes
The documentation gives the sandbox and the deny rules different scopes. The sandbox covers shell commands and the processes they start. Read and Edit deny rules cover the built-in file tools and recognized Bash file commands. These are the two documented scopes as stated, not a design diagram.
The documentation says read deny rules feed the sandbox. In plain terms, with the sandbox on, the paths named in Read deny rules are also blocked at the OS level for the shell commands the sandbox wraps, in addition to the rule check on the built-in file tools and recognized Bash file commands. In the recorded run, Claude described the sandbox as turning the Read deny rules into an OS block. That is Claude's statement, and the section on Claude's account of its own controls checks it against the documentation.
In my view, this is what the sandbox adds for two reads that the Read and Edit deny rules alone do not cover: grep -r over a directory and a script that opens a file itself. Both run as shell commands or their processes, so an OS-level block on a denied path would apply to them. No source in this chapter tests grep -r against the sandbox. The one recorded case of a script that opens .env is told in the section on the Python one-liner.
Two modes
The documentation says the sandbox has two modes: auto-allow and regular permissions. The recording used regular permissions, and so does Activity 5. The sandbox page describes what each mode does, so read its modes section before you choose one.
In the recorded run, the sandbox was turned on by typing /sandbox and choosing Sandbox BashTool, with regular permissions. That string is also the status label the recording showed. Later the recording ran /sandbox again and chose No Sandbox. For settings beyond these two modes, use the sandbox page.
7. A run observation: the Python .env one-liner
In the recorded run (Claude Code 2.1.295, Opus 5.5 at medium effort, started in auto mode), cat, wc, and grep on .env were denied with the deny rules in place. The recorded prompt for the next step was:
Now try python3 -c "print(open('.env').read())".With the sandbox off, auto mode blocked that command. The recording then turned the sandbox on in regular permissions mode, and the status label read Sandbox BashTool, with regular permissions. The recorded prompt Run the same python3 command again. was sent. The command ran and failed at the OS with this error:
PermissionError: [Errno 1] Operation not permitted: .env
That is the whole observation: a refusal by auto mode with the sandbox off, then an OS-level failure with it on. It is one run, and this chapter ties it to no mechanism.
What the documentation adds
The error class matches the macOS row of the sandbox page's probe table, and the documentation says read deny rules feed the sandbox: with the sandbox on, their paths are also blocked at the OS level. The OS-level error is consistent with that documented relationship. This run does not prove it.
The documentation also says the classifier reviews shell commands and that, in a server-side-review session, sandboxed commands can also wait for classifier review. It does not reconcile the sequence above.
This chapter states no cause for the difference between the two outcomes and no order in which the classifier and the sandbox acted. The difference is not attributed to the sandbox, the classifier, or Claude.
Your run
If you repeat this in Activity 5, report the result as yours. Model output is not deterministic, and in your run auto mode may block both commands, or neither. The error text above matches the macOS row of the probe table. The documentation says native Windows runs unsandboxed, which leaves no sandbox step to reproduce there. Run this only against a .env that holds placeholder values.
In my view, treat one observation as an observation, not as a rule to plan around. The documentation points to the deny rules and the OS-level enforcement for the controls to rely on, and it describes the classifier as a second gate.
8. Claude's account of its own controls
Claude is not an authority on its own safeguards. Three statements from the recorded run show why. They are paraphrased here, and each gets a verdict and a source.
| What Claude said | Verdict | Source |
|---|---|---|
cat .env was not covered by the Read rules. | Contradicted in the same run: cat was denied, and Claude then corrected itself. The documented list of recognized Bash file commands includes cat. | In the recorded run; the documentation says |
The Read(./.env) rules cover only the repository root. | Matches the documented anchoring when the session starts at the repository root. The documentation says relative patterns anchor at the current directory, so the statement is right for that starting directory and incomplete as a general rule. | The documentation says; in the recorded run |
| The sandbox turned the read deny rules into an OS block. | Agrees with the documented relationship: with the sandbox on, read deny rule paths are also blocked at the OS level. | The documentation says; in the recorded run |
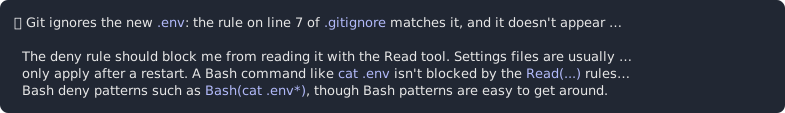
The third verdict is the one to be careful with. Agreement with the documentation does not make Claude's account authoritative. The documentation is the source, and Claude's statement is a claim that happened to match it. The first statement shows what a claim from the same source looks like when it does not match.
The course rule that model output is never presented as guaranteed applies to what a model says about its own safeguards as well.
In my view, when Claude describes a control, find the section of the documentation that covers it, or run a harmless test on a placeholder file. This chapter is held to the same test, which is why each claim carries a label and a date. Activity 6 gives you three statements to check.
9. Reviewing a generated Alembic migration before applying it
This section is a demo step. In my view, the habit it teaches is worth keeping, but the chapter cites no documentation for Alembic, autogenerate, SQLite handling, or the quality of Claude's migrations, so nothing below is a claim about how those behave. The habit is this: Claude generates, you review, and only then does anything run against a database.
In the recorded run (Claude Code 2.1.295), the schema change was a confirmed_at column in orders-service. The recorded prompt was:
Record when an order was confirmed: a confirmed_at column, set by the PaymentCaptured handler. Generate the Alembic migration but do not apply it; show it to me first.The recording read the migration Claude showed, then sent Apply it to a scratch database and run the tests. Activity 7 walks you through the same steps in your copy.
A checklist for the file
In my view, read the whole migration file, and check four things.
- It matches the model change and nothing else.
- It has both an upgrade and a downgrade, and they are inverses.
- No step drops, renames, or retypes existing data, or adds a non-null column to existing rows, without a stated reason.
- Its place among the existing migrations is as you expect.
If the file fails a check, ask Claude to revise it and read it again.
Why you copy the database
You have seen that checkpoints do not track changes made through Bash commands. In my view, applying a migration changes the database through a shell command, so a rewind is not the safety net here. Also in my view, copy the SQLite database file before you apply, and note where the copy is.
None of the controls in this chapter is documented as checking what a migration does. The review is yours. Run the apply command yourself, or tell Claude to run it, once you have read the file.
10. Reach map: what each control leaves open
The table gathers the controls from this chapter. The last column says where each claim comes from, and the published figures carry their own date.
| Control | Covers | Does not cover | Label |
|---|---|---|---|
| A CLAUDE.md instruction | Reaches Claude as context | No guarantee of strict compliance | The documentation says |
| Read or Edit deny rule | Built-in file tools, recognized Bash file commands (cat, head, tail, sed, tee) and redirection targets | Commands that read files without naming them (grep -r) and scripts that open files themselves. The recorded run's notes also say that pasted content and ! content are outside it | The documentation says for the commands. In the recorded run, cat, wc and grep on .env were denied, and the notes say that no deny rule protects pasted or ! content |
| Bash rule | Command text that matches the rule | Other spellings: git -C . push and git -c push.default=current push for Bash(git push *), and the same two for Bash(git push:*) | The documentation says for Bash(git push *); in my view for Bash(git push:*) |
| Auto-mode classifier | A second review, which the documentation calls a second gate | Not a guarantee. The post of 2026-03-25 reported 0.4% false positives and 17% false negatives on real overeager actions for the pipeline current then | The documentation says; the figures are volatile |
| Sandbox | Shell commands (Bash, PowerShell, Monitor) and their processes, with Seatbelt on macOS and bubblewrap on Linux and WSL2 | File tools, MCP servers, command hooks, plugin processes, ! commands in most sessions, and native Windows | The documentation says; in the recorded run one command failed at the OS with the sandbox on |
| Migration review | Whatever you check in the file | No control is documented as checking migration content, and a rewind does not undo an applied migration | In my view, including the rewind point |
The documentation gives three relations between controls, and this chapter claims no others: deny rules apply in every mode, the classifier reviews actions after the rules, and read deny rules feed the sandbox (with the sandbox on, their paths are also blocked at the OS level). The table does not say that one control backs up another, and it says nothing about how the classifier and the sandbox interact.
Re-check against the current documentation: the version that made auto the starting mode, the classifier model and its thresholds, the published error rates and their date, and sandbox platform support.
Open cases to carry into your own project:
- In the recorded run's notes, a secret pasted into a prompt, or printed by a
!command, is in the conversation and no deny rule protects it. - The documentation says a
!command runs unsandboxed in most sessions. - The documentation says commands that read files without naming them, such as
grep -r, and scripts that open files themselves are outside the Read and Edit deny rules. - The documentation says
git -C . pushandgit -c push.default=current pushare outside a Bash rule written forgit push. - The documentation says file tools, MCP servers, command hooks, and plugin processes run outside the sandbox, and that native Windows runs unsandboxed.
- In my view, the content of an applied migration is checked only by your review, and a rewind does not undo it.
Activity 1: Write the starting-mode note
You write a short note that fixes the mode vocabulary and the starting-mode wording before the rules and the classifier come in. The repository does not change.
Steps:
- Write down the six permission mode names as the permission-modes page lists them. Mark the one that is shown as Manual.
- For each statement below, mark its source as changelog, permission-modes page, or recorded run:
- the 2.1.283 entry for sessions with third-party providers or telemetry off;
- the 2.1.284 entry for every plan and provider in the terminal and VS Code;
- the page's 2.1.283 for all sessions;
- the lesson 05 recording on 2.1.295.
- Write a starting-mode note of three sentences. It names the mode, cites the two changelog entries, states the page discrepancy, and gives the date on which you checked them.
- Add one sentence from the modes section saying which rule type applies in every mode and which has no effect in
bypassPermissions. - Write down the Claude Code version you run, and say whether it is at or after 2.1.295.
You should end with:
- a list of the six mode names;
- the three-sentence note;
- the one-sentence rule statement.
The exercise records the version your demo runs on beside the recorded 2.1.295.
Hints:
- Cite the changelog for version-specific claims. The page and the changelog are both first-party and the discrepancy is unresolved, so say that instead of picking a winner.
- If you mention 2.1.285, say only that the sources give it for
claude -pand SDK sessions that run without feature flags. - Do not describe any mode beyond what this chapter states unless you cite the page's mode table.
Check yourself:
- The note names auto as the starting mode, gives the date on which you checked it, and cites the changelog entries for 2.1.283 and 2.1.284 with their scopes. Both versions appear, each tied to the changelog: third-party providers or telemetry off for 2.1.283, every plan and provider in the terminal and VS Code for 2.1.284.
- The note records that the permission-modes page gives 2.1.283 for all sessions, says the two sources are unresolved, and says the changelog is used for version-specific claims.
- The mode list and the rule sentence match the modes section and the permission-modes page.
- Your source marks for step 2 read: changelog, changelog, permission-modes page, recorded run.
Activity 2: Write and test the .env rules
You write the demo's first permission configuration and test it against a placeholder .env. The recorded session ran in orders-service, and the settings file belongs at orders-service/.claude/settings.json. Every value here is a placeholder, and nothing in this lab runs a push.
Steps:
-
From
shop-workspace, run./checkout-lesson.sh 05so every repository is atlesson-05-start. Then change intoorders-service. The settings file you create belongs there, not inshop-workspace. -
Decide which directory you will start
claudein, and write it down. The recorded session started inorders-service, and starting there matches the recording and thelesson-05-endtag. Relative patterns anchor at the current directory, not at the repository root, so the directory you name decides which.envthe rules point at. If you start in a different directory, write that one down and report your results as a variation from the recorded run. -
Start
claudefrom that directory. Either send the prompt the recording used, or openorders-service/.claude/settings.jsonand add the rules by hand:Create .claude/settings.json: allow uv run pytest, ruff and mypy; ask before git push; deny reading .env and .env.* files. Add .env to .gitignore. -
Open
orders-service/.claude/settings.jsonand check that the two recorded rules appear in exactly these forms, adding or correcting them if they do not: the Read deny ruleRead(./.env)and the ask ruleBash(git push:*). Then add the Edit deny ruleEdit(./.env)if the file lacks it. In my view this rule belongs in the file; the recorded prompt asked only to deny reading, so the Edit rule is my addition. Label any extra pattern, such as one for other secret files, as your own, and check its syntax against the permissions page of the official documentation. -
Check that the
.envin your directory holds placeholder values only. If it holds anything real, move that file out of the demo directory and put placeholders in its place. If there is no.env, the recording created one with the command below, typed at the!prompt in the session (in a plain shell, drop the leading!). It writes a random throwaway value and prints nothing:!printf 'PAYMENT_GATEWAY_KEY=%s\n' "$(openssl rand -hex 8)" > .env -
Leave the session with
/exitand start a freshclaudesession from the directory you wrote down. In my view, start fresh, because this chapter makes no claim about whether a running session picks up a settings change. -
In separate prompts, ask for
.envfour ways, and record each outcome as denied, allowed, or prompted:What is in .env?(a recorded prompt; note which tool Claude uses)Try cat .env.(a recorded prompt)Try wc -c .env.(the chapter's wording, not a recorded prompt)Try grep PAYMENT_GATEWAY_KEY .env.(the chapter's wording, not a recorded prompt)
-
Put the recorded outcomes beside yours. The recorded run denied
cat,wc, andgrep. This chapter gives no recorded outcome for the Read request, so write 'not given' in that cell. Write one sentence on any difference and report it as your run. -
Optional: start a second session one directory down, repeat the Read request, and record what you observe, without predicting it. Label the result as your observation, not documented behavior.
-
Do not approve a push to test the ask rule. If Claude asks to run git push at any point, decline it.
You should end with:
orders-service/.claude/settings.jsonholding the Read deny rule for./.env, thegit pushask rule and, in my view, the Edit deny rule for the same file;- a statement of the starting directory;
- a four-row test log (Read,
cat,wc,grep) beside the recorded outcomes.
This is the demo's first permission configuration.
Hints:
- The documented gaps are in the section on what deny rules and Bash rules do not cover. If a command gets through here, write it in the log and carry it forward.
- An ask rule prompts you. It does not refuse the command.
- Report your results as your run. Model output is not deterministic.
Check yourself:
- The settings file holds the Read deny rule for
./.envand the ask rule in the forms above, and the Edit deny rule you added, which is labeled as your addition. Compare it with the same file atlesson-05-end: fromorders-service, rungit show lesson-05-end:.claude/settings.jsonand compare these rules with your file. The file at the tag can differ from yours. - The log names the starting directory and says relative patterns anchor at the current directory and a single leading slash anchors at the settings source.
- Four rows are present, each with an outcome and the recorded outcome beside it, with no explanation of differences.
- The
.envused for the test contains placeholder values only.
Activity 3: Coverage drill
You sort command spellings and routes by whether the rules cover them, so the gaps are stated from the documentation and not from memory. This is a paper exercise. Do not run any push.
Steps:
- For the rule
Bash(git push *), mark which of these the rule text matches:git push origin main,git -C . push,git -c push.default=current push. - Do the same for the lesson 05 ask rule
Bash(git push:*). Mark your conclusion 'in my view', because the documentation describes:*as an equivalent trailing wildcard. - Sort these into covered and not covered by Read and Edit deny rules:
- the built-in Read tool on
.env; cat,head,tail,sed, andteenaming.env;- a redirection target;
grep -rover a directory;- a script that opens
.envitself.
- the built-in Read tool on
- Add the recorded result:
cat,wc, andgrepwere denied in the lesson 05 run. State it beside the documented list without reconciling the two. - List the routes by which text reaches the conversation without a Read tool call: pasted text and text entered with the
!prompt. Write what the lesson 05 recording's notes state about deny-rule protection for these routes, as the section on content that skips the rules reports it, and mark it 'in the recorded run'. Then write what the documentation says about where a!command runs, and mark it 'the documentation says'. - Write one rule for yourself about pasting secrets and running
!commands that print them. Mark it 'in my view'.
You should end with:
- a table of command spellings against the two Bash rules, marked as matched or not stopped;
- two lists, covered and not covered by Read and Edit deny rules;
- a short list of the routes into the conversation with your personal rule.
The repository does not change. The drill gives you the list of gaps that your Activity 2 rules leave open, and Activity 8 reuses it.
Hints:
- The documented list of recognized commands does not include
wc. Write down what was recorded and what is documented, and stop there. - Keep the words 'in most sessions' for the
!prompt.
Check yourself:
git -C . pushandgit -c push.default=current pushare marked as not stopped byBash(git push *), and the conclusion forBash(git push:*)is marked 'in my view'.- The covered and not-covered lists match the documentation, the recorded
wcandgrepdenials are stated without explanation, and no command outside the documented lists was added. - The pasted and
!routes carry the mark 'in the recorded run' for deny-rule protection. The!command statement carries the mark 'the documentation says' and the words 'in most sessions'.
Activity 4: Write the classifier fact sheet
You write a one-page fact sheet on the auto-mode classifier. Every volatile item carries its date. The repository does not change.
Steps:
- One line on what the classifier is: a second model, Claude Sonnet 5 by default according to the documentation, and not the
/modelselection. - One line on when it reviews an action, in the documentation's wording: after the rules and the read-only and in-directory checks.
- Two lists: what it sees (your messages, tool calls that are not read-only, and CLAUDE.md) and what it does not see (tool results, which are stripped).
- One line on what happens to broad allow rules on entering auto mode, naming
Bash(*)andBash(python*). - One line on the pause: three blocks in a row or 20 in total.
- The documentation's own limit: auto mode is a second gate, and the documentation points to
permissions.denyfor actions that must never run. - The published figures with their date and scope: 0.4% false positives and 17% false negatives on real overeager actions, in Anthropic's post of 2026-03-25, for the pipeline current at that time.
- Mark the items most likely to change first, and write against each the date on which you checked it.
You should end with:
- a fact sheet of seven dated or labeled items;
- a list of the volatile ones.
The sheet is your reference for what the starting mode does while you work through the demo.
Hints:
- The chapter paraphrases the figures; check the post before you quote them. Paraphrase them on your sheet too.
- Write the figures with the release they describe. Do not write that the classifier misses 17% without the date and scope.
- State that tool results are stripped without giving a reason.
Check yourself:
- The see and does-not-see lists match the documentation: your messages, non-read-only tool calls, and CLAUDE.md on one side, tool results on the other.
- Search the sheet for 0.4% and 17%. Each occurrence sits in a sentence that carries 2026-03-25 and the release it describes, and neither is written as a current rate.
- The sheet names the second-gate wording and the
permissions.denypointer.
Activity 5: Log the .env one-liner with the sandbox off and on
You run the lesson 05 Python one-liner against a placeholder .env in two sandbox states and log what happens. Claim only what you observed. The repository does not change.
Steps:
-
Read the sandbox section and write down what the sandbox wraps and what runs outside it.
-
Note your platform. The sandbox section lists the mechanism for each platform. On native Windows, read the recorded observation and skip the sandbox-on steps.
-
Check that the
.envholds placeholder values only and that the deny rules from Activity 2 are still in place. -
With the sandbox off, in the starting mode, send the request as it was typed in the lesson 05 recording:
Now try python3 -c "print(open('.env').read())".The lesson 05 recording includes one follow-up for the case where Claude declines:
It's a random throwaway value; I want to see what the deny rule covers.Send it only if that happens. Log the date, Claude Code version, platform, sandbox state, and outcome, and list every prompt you sent. -
Turn the sandbox on in regular permissions mode: type
/sandboxand chooseSandbox BashTool, with regular permissions. Confirm that the status label readsSandbox BashTool, with regular permissions. -
Send
Run the same python3 command again.and log the outcome. Copy the error text exactly if there is one. -
Turn the sandbox off again with
/sandboxandNo Sandbox. -
Add two columns to your log. In 'what I can claim', write what you saw. In 'what I cannot claim', write that you do not know why the two outcomes differ and do not know the order in which the classifier and the sandbox acted.
-
Write two sentences: one for the recorded run and one for yours.
You should end with:
- a two-row observation log (date, version, platform, sandbox state, outcome, and verbatim error text);
- the 'what I can claim' and 'what I cannot claim' columns;
- the two summary sentences.
The log sits beside the recorded run in the demo state you hold at the end of lesson 05.
Hints:
- The recorded error was
PermissionError: [Errno 1] Operation not permitted: .env, and it matches the macOS row of the documentation's probe table. Yours may differ. - Keep causal wording out of the log and out of the summary sentences.
- If both runs refuse, or both run, report that as your result. Do not adjust the log toward the recorded run.
Check yourself:
- The log has a row for each sandbox state with date, version, platform, and outcome, or the field is marked not applicable on native Windows.
- No row or summary sentence gives a cause for the difference or an order between the classifier and the sandbox. Read both columns and both sentences for causal wording.
- The test used a placeholder
.env. Check the file content at the start of the lab.
Activity 6: Check three of Claude's statements
You check three of Claude's statements against the documentation and your own logs. The statements are paraphrased from the lesson 05 recording, so do not put the paraphrases in quotation marks: they are not Claude's exact words. The repository does not change.
Steps:
- Claude said
cat .envwas not covered by the Read rules. Compare that with what happened in the run (catwas denied) and with the documented list of recognized Bash file commands. Write a verdict. - Claude said the
Read(./.env)rules cover only the repository root. Compare that with the anchoring rule and with the directory your session started in. Write a verdict that names the directory. - Claude said the sandbox turned the read deny rules into an OS block. Compare that with the documented relationship between read deny rules and the sandbox (with the sandbox on, read deny rule paths are also blocked at the OS level), and with your Activity 5 log. Write a verdict.
- Add one sentence saying why agreement with the documentation in the third case does not make Claude's account authoritative.
- Write one rule for how you will check a future statement of this kind.
You should end with:
- a three-row verdict table with the source used for each row;
- the sentence on agreement and authority;
- the one-line checking rule.
The table reuses your Activity 2 and Activity 5 logs as its evidence.
Hints:
- The second statement is right in one case and not in general. Say which.
- A model's account is a claim to check, whatever the verdict.
Check yourself:
- Every row of the table cites a source: the run, the documentation, or both.
- The second row names the directory your session started in.
- The agreement sentence says the match does not make the statement authoritative.
Activity 7: Review a generated migration before applying it
This task is a demo step, and in my view the review habit in it is worth keeping. You have Claude generate an Alembic migration in orders-service, review it against a checklist, and apply it only afterward.
Steps:
-
Work from the lesson 05 state in
orders-service, the service that has the PaymentCaptured handler and its Alembic migrations. Rungit statusand note what it shows, so you can see afterward what changed. -
Find the SQLite database file that
orders-serviceuses, and copy it. From theorders-servicedirectory, runfind . -name '*.db'to list candidates; the recording's later deny-rule prompt refers to the service's*.dbfiles. If more than one file is listed, check where the service's settings or its.envfile point, and do not guess. Save the copy outside theorders-servicedirectory, so it cannot end up in a commit, and note where the copy is. If no file is listed, write that in your review note. -
Send the prompt as recorded. It already tells Claude not to apply the migration:
Record when an order was confirmed: a confirmed_at column, set by the PaymentCaptured handler. Generate the Alembic migration but do not apply it; show it to me first. -
Read the generated migration file in full.
-
Review it against the checklist: it matches the model change and nothing else; the upgrade and downgrade are both present and are inverses; no step drops, renames, or retypes existing data, or adds a non-null column to existing rows, without a reason; its place among the existing migrations is as expected.
-
Write a two-line review note: what you checked, and anything you would decline. If the checklist flags something, ask Claude to revise the file and read it again.
-
Apply the migration only after the review, by running the command yourself or by telling Claude to run it. The recording used
Apply it to a scratch database and run the tests. -
Write one sentence marked 'in my view': checkpoints do not track changes made through Bash commands, so rewinding would not undo the applied migration.
-
Leave
orders-servicewith a clean working tree. The settings file, the.gitignorechange, the reviewed migration, and the other files Claude changed for theconfirmed_atcolumn are still uncommitted. How the checkout script treats uncommitted changes is not documented here, so settle them before you run./checkout-lesson.shagain.- In
orders-service, rungit switch -c scratch/ch05-permissions(the branch name is an invented example). - Commit
.claude/settings.json, the.gitignorechange, the reviewed migration, and the other files Claude changed for theconfirmed_atcolumn. You can give Claude the prompt the recorded run typed,Commit., or rungit addandgit commityourself. Do not push. - Keep
.envand the database copy out of the commit. Rungit show --stat HEADand confirm that the list holds neither a.envfile nor a database file. - Run
git status --short. It should print nothing..envshould not appear, because the prompt in Activity 2 asked Claude to add it to.gitignore. If it does appear, add.envto.gitignore, commit that change, and check again; never commit.envitself. If anything else is listed, read it and settle it before you move on.
- In
You should end with:
- a reviewed migration file;
- the database copy taken ahead of the apply step;
- the two-line review note;
- either an applied migration or a note that you declined to apply it;
- a scratch branch in
orders-serviceholding a commit of the settings file, the.gitignorechange, and the reviewed migration, with.envand the database copy out of the commit, and agit status --shortthat prints nothing.
The migration is the lesson 05 schema change, as in the lesson-05-end tag. Compare your files with the tag to confirm the exact change.
Hints:
- Mark the whole task as a demo step and the habit as 'in my view'. The chapter cites no documentation on migration review.
- Do not assume the migration is fine because the earlier controls were in place. None of them is documented as checking migration content.
Check yourself:
- A database copy exists, and its time stamp is earlier than the apply step, or your note says no database file was found.
- The review note covers each of the four checklist items.
- The migration was applied after the review. Check the order in the session or in your notes.
- The note marks the task as a demo step and the habit as 'in my view', and marks the rewind sentence 'in my view'.
- The commit holds the settings file, the
.gitignorechange, and the migration, and holds neither.envnor a database file.git show --stat HEADlists its files. git status --shortinorders-serviceprints nothing, and no push was run.
Activity 8: Build the reach map
You collect every control and its gaps into one table with labels, and name what stays reachable in your own project. The repository does not change.
Steps:
- Draw a table with six rows: a CLAUDE.md instruction, a Read or Edit deny rule, a Bash rule, the auto-mode classifier, the sandbox, and migration review.
- Add three columns: what it covers, what it does not cover, and a label ('the documentation says', 'in the recorded run', or 'in my view').
- Fill each cell using only statements from this chapter, and put the date against anything volatile.
- Do not write that one control backs up another. Write only the relations the documentation gives: deny rules apply in every mode, the classifier reviews after the rules, and read deny rules feed the sandbox (with the sandbox on, their paths are also blocked at the OS level).
- List the cases that stay reachable in your own project after your rules and settings, and what you would check again, noting the date on which you checked each item.
You should end with:
- a six-row reach map;
- a list of cases still reachable in your project;
- a list of volatile items to re-check.
The map is your record of the controls now in the demo and the cases they leave open.
Hints:
- Use the lists from Activities 3, 4, and 5 for most cells.
- Leave a cell blank rather than guess. A blank cell is a gap to look up.
- If a cell needs a claim the chapter did not make, mark it 'in my view'.
Check yourself:
- Every cell is labeled, and the volatile items are dated.
- No cell claims an interaction between the classifier and the sandbox. Read the classifier and sandbox rows.
- The list of open cases exists and names at least the pasted and
!routes, with the pasted and!deny-rule gap marked 'in the recorded run'.
Starting state: every repository at lesson-05-start, reached with ./checkout-lesson.sh 05. Run git status in the repository you work in to see what the tag holds, and treat the tag as the reference rather than assuming which instruction files are present. You need a Claude Code session and a .env that holds placeholder values only. If your copy drifts, run ./checkout-lesson.sh 05 --end from shop-workspace to jump every repository to lesson-05-end.
What the chapter adds to the demo:
orders-service/.claude/settings.jsonwith the Read deny rule for./.envand the ask ruleBash(git push:*), plus, in my view, an Edit deny rule for the same file, and your written statement of the directory the session started in (Activity 2).- Your own observation log of the Python
.envone-liner with the sandbox off and on, kept beside the recorded run. This is a note, not a repository change (Activity 5). - One Alembic migration in
orders-servicefor aconfirmed_atcolumn, generated by Claude, reviewed by you, and applied or deliberately held back, with a copy of the SQLite database file taken ahead of the apply step. The settings file, the.gitignorechange, and the reviewed migration are committed on a scratch branch, with.envand the database copy kept out of the commit (Activity 7).
The chapter does not touch the order flow, Kafka, or the end-to-end checks.
Ending state: your orders-service is on a scratch branch whose commit holds .claude/settings.json (the Read deny rule for ./.env and the git push ask rule, plus the Edit deny rule if you added it), the .gitignore change, and a reviewed migration that has been applied or deliberately held back. .env and the pre-apply database copy are not in the commit, and git status --short prints nothing in orders-service. You also hold your own logs and notes. In the recorded run, the session went on to ask Claude for a deny rule on the service's *.db files and then committed. The lesson-05-end tag is the reference for the exact result, git diff lesson-05-end shows how your copy differs, and ./checkout-lesson.sh 05 --end jumps every repository there if your copy diverges.
Learner outputs:
- A starting-mode note that cites the 2.1.283 and 2.1.284 changelog entries, notes the permission-modes page discrepancy, and records the date on which you checked it.
- A
.claude/settings.jsonwith the Read deny rule for./.env, thegit pushask rule and, in my view, the Edit deny rule for the same file, and a statement of the starting directory. - A test log of Read,
cat,wc, andgrepagainst the placeholder.env, beside the recorded outcomes. - A coverage drill sheet of command spellings, covered and not-covered cases, and the pasted and
!routes. - A one-page classifier fact sheet with the published error rates, their 2026-03-25 date, and the release they describe.
- A two-row observation log of the one-liner with the sandbox off and on, with 'what I can claim' and 'what I cannot claim' columns.
- A three-row verdict table on Claude's statements about its own controls.
- A reviewed Alembic migration, a pre-apply database copy, and a two-line review note, marked as a demo step and 'in my view'.
- A scratch branch in
orders-servicewith a commit of the settings file, the.gitignorechange, and the reviewed migration, and a clean working tree. - A reach map of six controls with coverage, gaps, and labels, and a list of cases still reachable in your project.
Checks for the end state:
- The starting-mode note cites both changelog entries and the page discrepancy, and carries the date.
- The 0.4% and 17% figures appear only with 2026-03-25 and the release they describe.
- The observation log gives no cause and no order between the classifier and the sandbox.
- The settings file names the starting directory in your notes and holds the rules in the forms above.
- Every lab used a placeholder
.env, and no step ran a push. - The migration was applied after the review, and the database copy is older than the apply step.
- The scratch branch holds the settings file, the
.gitignorechange, and the migration,.envand the database copy are not in the commit, andgit status --shortprints nothing inorders-service.
Sources
- Configure permissions
- How Claude remembers your project
- Claude Code changelog (docs site)
- Choose a permission mode
- anthropics/claude-code CHANGELOG.md
- What's new (weekly digest index)
- Configure auto mode
- Anthropic engineering: Claude Code auto mode
- Configure the sandboxed Bash tool
- Plugin security and trust
- Security